You Handed Your ID to the Bouncer. You Won't Hand It to Google.
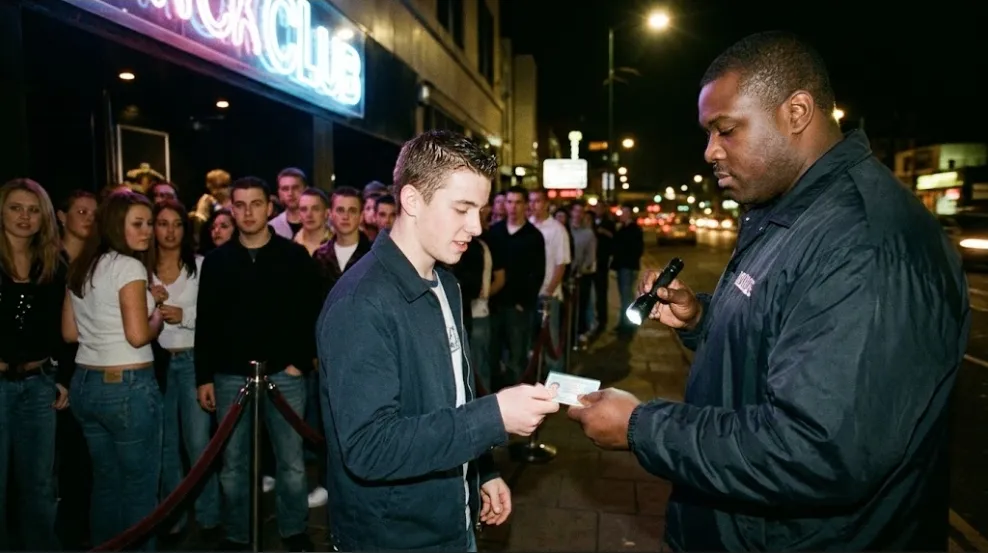
Think back to the night you turned eighteen. You stood outside a loud, sticky-floored nightclub in the dark, bouncing on your heels, practically begging to hand your government ID over to a complete stranger standing behind a velvet rope. You did not know his name. You did not ask to see his data retention policy. You had no idea whether he worked for the club, worked for a shady security contractor, or was memorizing your home address while shining a flashlight in your face. You handed it over with a grin because you wanted to get inside, buy overpriced drinks, and maybe go home with somebody attractive.
Fast forward ten or twenty years, and that exact same person is having a full-blown meltdown online because Google wants to verify their account or X asks for proof of identity. Suddenly, handing over an ID is the opening chapter of a dystopian nightmare. Suddenly, Silicon Valley is out to destroy their freedom, and Elon Musk is sitting in a volcano lair personally plotting their downfall.
That is not threat modeling. That is vibes.
Most internet privacy discourse today is not actually about security. It is about ego. People love to imagine that a team of engineers in Mountain View is huddled around a monitor sipping espresso, listening to their bedroom microphone to see if they had sex last night, or tracking what time they finally rolled out of bed on a Saturday morning. Let me save you some stress: nobody at Google cares about your sex life. Nobody is watching you sleep in. You are not a character in a Jason Bourne movie. To a trillion-dollar advertising engine, you are a cluster of behavioral signals inside an automated auction system, not a person anyone wants to spy on over lunch.
Self-interest is not charity, and that is actually good news
Now, do not mistake that for a defense of Big Tech's morality. Google is greedy. Corporations are selfish by design. Anyone pretending these companies act out of pure altruism is selling you something.
Then again, let us be honest about human nature for five seconds. Remember those old reality shows like Survivor, where two strangers get stuck on an island together and start making noble pacts? "Bro, if we make it to the final two, I swear I will split the million dollars with you 50/50." People love watching that stuff and pretending they would honour the handshake. Most of us know better. If a million dollars is sitting on the table and you have a family to feed, the real answer is simple: forget the pact, I am looking after numero uno.
Google plays by the exact same rule, just at global scale. And in cybersecurity, predictable self-interest is actually one of the most reliable defenses you can ask for.
Think about the actual incentives. Google is not going to take your raw location history and sell it to some random lunatic on the internet just to ruin your Tuesday. Why? Not because they love you, and not because they are saints, but because leaking raw user identities to bad actors destroys their business model. Also, remember they are greedy, and a threat actor pays less than a monopoly 3rd party.
Advertisers pay Google to keep the data inside the vault and serve targeted ads without ever handing over the keys. A scandal where Google directly hands your personal movements to stalkers would invite catastrophic lawsuits, regulatory crackdowns, and mass user flight. Self-interest keeps that vault bolted shut far better than corporate ethics statements ever could.
What verification actually looks like in the real world
People love treating platform verification like an ideological war until reality taps them on the shoulder.
Take my own experience on X. If you spend enough time online saying things people do not like, you get mass-reported for being controversial. On top of that, I had been actively reporting CSAM on the platform, because when you see filth like that, you flag it and get it nuked. The next morning, I woke up logged out of my account. The screen gave me the standard warning: irregular usage detected, sign back in, provide proof of identity.
At that moment, you have a choice. You can throw your phone against the wall, write a twelve-paragraph rant about how Elon Musk is building a surveillance state, and burn your account to the ground. Or you can think like an adult and weigh the actual risk against the actual reward.
X routes identity verification through a third-party verification vendor (companies like Persona handle a massive chunk of this KYC infrastructure across the web). I uploaded my driver's licence. They accepted it. They asked for a live video selfie to match the face to the document. I did that too. Five minutes later, I had my account back, along with my blue check and green verification badge.
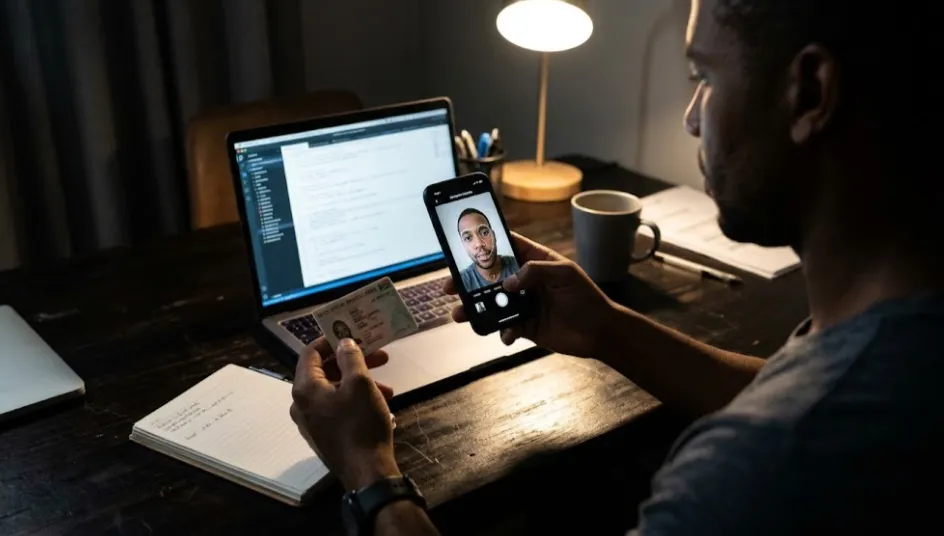
Did I love handing my driver's licence to a third-party contractor? No. Was it an acceptable trade to recover an account I use every day for research and publishing? Yes. We make risk-reward trades like that every single week when we check into a hotel, rent a car, open a bank account, or hand our ID to a bouncer at eighteen. Pretending a tech platform is uniquely demonic for doing the same thing just shows you have not actually thought through where real threats come from.
Now let us look at the other side of the coin
If this essay stopped here, it would be one-sided garbage. Because here is the uncomfortable truth that the "just relax, nobody cares about you" crowd always misses: your data does get out, and malicious actors do find ways to hurt regular people with it.
They just rarely get it by asking Google nicely.
If you want to stop being paranoid about imaginary problems and start protecting yourself from realistic ones, you need to understand the actual pipelines where regular people get burned.
1. The person you just insulted in a Facebook comment section. This is the single biggest blind spot on the modern internet. You will see someone spend three hours hardening their phone settings to hide from Google, and then ten minutes later they hop on Facebook under their full government name and start calling an unstable stranger a moron in a public comment thread.
A motivated idiot with an axe to grind does not need to breach Google's data centers to ruin your week. They just click your profile. Your friends list is public. Your city is listed under your bio. Your wife's account is tagged in your anniversary post. You uploaded a photo of your new car in your driveway with half the street sign visible in the background. Within twenty minutes of basic open-source intelligence (OSINT), someone who genuinely hates you knows where you live, where you work, and what your kids look like.
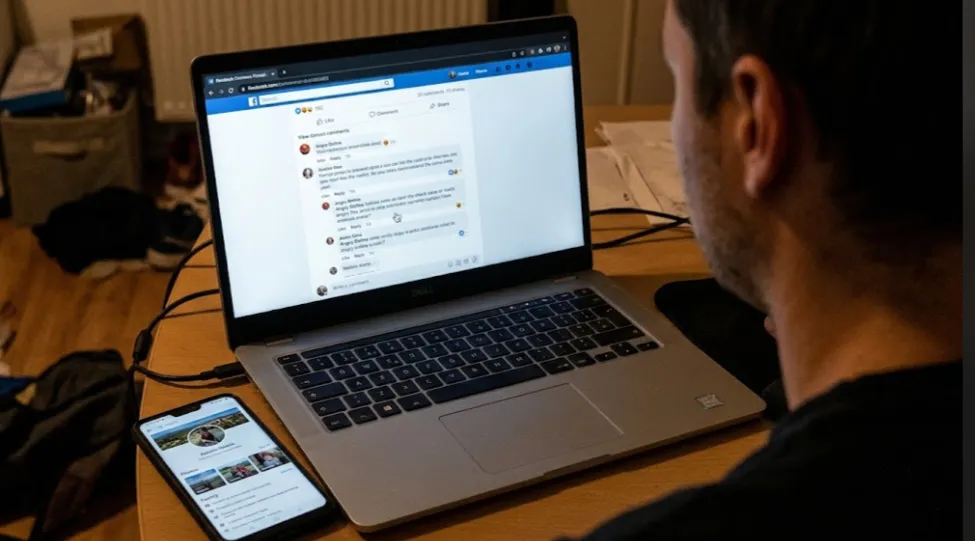
Google has billions of dollars on the line to keep your data safe. The guy you just humiliated in a comment section has nothing to lose and all weekend to dig through your digital footprint.
2. Third-party SDKs and the data broker sewer. Google does not sell your raw GPS coordinates to random buyers. That does not mean your phone's location is not for sale.
Every time you install a free flashlight app, a sketchy weather widget, a barcode scanner, or a hyper-casual mobile game and tap "Allow Location Always," you are often feeding third-party software development kits (SDKs) baked inside those apps. Those SDKs harvest precise latitude and longitude pings in the background and sell them upstream to commercial data brokers, a pipeline the Electronic Frontier Foundation and privacy researchers have documented repeatedly. Anyone with a corporate email address and a credit card can buy commercial location telemetry from brokers and de-anonymize it in minutes. If you leave location permissions wide open for junk apps, you are leaking the exact trail you were terrified Big Tech might misuse.
3. Third-party vendors and secondary breaches. Remember that third-party verification step on X? That is actually where a smart skeptic raises an eyebrow, and rightly so.
Major tech giants spend billions hardening their core infrastructure. The weak links are almost always the smaller third-party contractors, forum databases, local retailers, and verification vendors sitting around the edges. When a third-party company gets breached and dumps ID scans or customer records onto a dark web forum, it is not because they were "evil." It is because security is hard, retention policies get ignored, and smaller vendors cut corners. Accepting that trade means being selective about who gets your documents and never assuming a third-party portal deletes your files the second the checkmark appears.
4. Account takeover because you left the keys under the mat. If a malicious actor wants your Google Timeline, your private photos, and your email archive, they are not going to exploit a zero-day vulnerability in Google Cloud. They are going to grab your old password from a shopping site that got breached four years ago, test it against your email address, and walk straight through the front door. Verizon's Data Breach Investigations Report and Cloudflare's traffic telemetry hammer this home year after year: compromised credentials remain one of the easiest front doors on the internet. Or an attacker will send you a convincing phishing text about a missed delivery and wait for you to type your login credentials into a fake page.
Once someone compromises your account, Google is no longer your adversary. Your own convenience features become their surveillance toolkit.
5. Legal compulsion and state power. Finally, there is one legitimate way data stored inside Google or X leaves those servers without a hack: a subpoena or a warrant. Governments issue geofence warrants, account record demands, and emergency disclosure requests every single day. Google eventually migrated its old Sensorvault Location History on-device so it could no longer answer classic geofence requests, and the U.S. Supreme Court built on its landmark Carpenter v. United States precedent with its June 2026 Chatrie v. United States ruling, holding that police acquisition of Google Location History through a geofence warrant constitutes a Fourth Amendment search.
Notice the difference, though. Worrying about overreaching government warrants is a rational conversation about law and civil liberties. Worrying that a Google intern is secretly watching you sleep with your spouse is a distraction that keeps you from fixing your actual vulnerabilities.
Fix your threat model
Privacy is not a purity test, and paranoia is not security. You cannot live off the grid while carrying a smartphone in your pocket, and pretending you can usually leads to sloppy habits in the places that actually matter.
Keep your skepticism sharp. Question what Big Tech collects, support stronger laws around data brokers, lock down your accounts with unique passwords and hardware passkeys, strip location access away from junk apps, and think twice before handing your real identity to strangers in a public comment war.
Just stop acting like the bouncer at the nightclub was your best friend while Google is hiding under your bed. Know who actually wants to hurt you, know how they actually get your information, and guard the doors that actually open. Adjacent to private is not private.
Sources and scope. Electronic Frontier Foundation and related reporting on location data brokers and SDKs in free apps. Verizon Data Breach Investigations Report and Cloudflare measurements on credential stuffing and account takeover. Reporting on Google's migration of Location History to on-device storage and the U.S. Supreme Court's Fourth Amendment location-privacy decisions in Carpenter v. United States and Chatrie v. United States. This piece distinguishes documented commercial data-broker pipelines, credential-based account compromise, and public self-exposure from claims of routine raw-identity sales or continuous human monitoring by platform staff. It does not treat platform self-interest as moral virtue, nor does it claim that legal process cannot compel data under warrant.
Interpretation of relative risk priority is mine.
Clayton Bax
Published under ONYX Digital Intelligence Following the #OnyxAudit methodology.
- X: @OnyxAudit
- Email: onyxdigitalintelligence85@protonmail.com
- https://github.com/Baximus855
- @Onyx_Digital@mastodon.social
"Adjacent to true is not true."
Truth has no flag nor favour, only a standard. And it's heavy!
Editors note: I use various AI agents to fetch my research. I check, strip and write the article. Facts are partly theirs. Interpretation is mine.