Linux Kernel TCP UAF (CVE-2026-98432) Lets Anthropic's Model Build a Remote Root Chain on MPTCP Listeners
CVE-2026-98432 is a race-condition use-after-free in the Linux kernel's IPv4 TCP handshake path. Ownership of ireq_opt is transferred to the child socket (inet_opt) without a proper RCU grace period before the request socket can be freed. The kernel CNA rates it 9.8 (AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). It affects kernels from the 4.4 era forward until the relevant stable branch is patched. Upstream fixed it on 15 October 2026 (commit that frees inet_opt and ireq_opt after an RCU grace period). Fixed stable releases include: 5.10.272 5.15.223 6.1.190 6.6.159 6.12.113 6.18.56 7.2.10 7.3
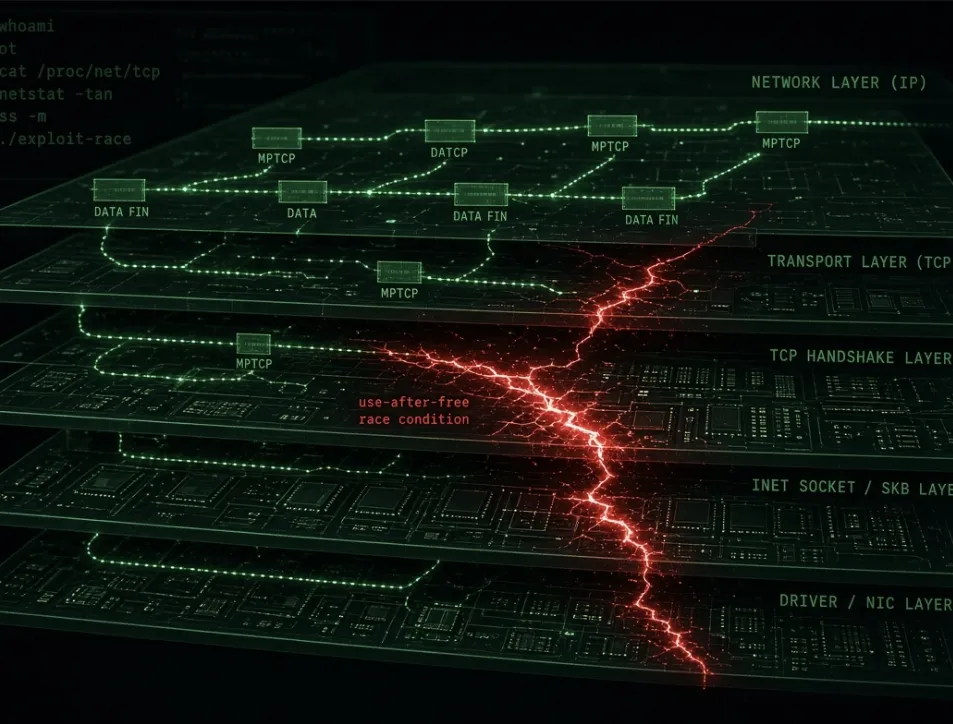
What Anthropic demonstrated On 28 October 2026 Anthropic's Frontier Red Team stated that an unreleased Claude research model turned the bug into a working zero-click remote root exploit against servers that have a Multipath TCP (MPTCP) listener. In their lab the chain took roughly 48 minutes to leak a kernel address (defeating KASLR) and another five minutes to reach a root shell. A lost race simply fails the handshake; the attacker retries. The exploit was built in a controlled environment. There is no public evidence of in-the-wild use and it is not in CISA's Known Exploited Vulnerabilities catalog. The demonstrated chain requires an MPTCP listener. Check with:
sysctl net.mptcp.enabled ss -Mltn
A host with MPTCP disabled or with no MPTCP listener is not reachable by the specific chain Anthropic published. The underlying UAF exists in general TCP handshake handling, so treat the bug as more than an MPTCP-only issue. Distribution status (as of 29 October 2026) Debian: Fixed. Bookworm 6.1.190-1, Trixie 6.12.113-1 (and related linux-6.12 packages). Oracle Linux (UEK): Errata published 16 October 2026 (ELSA-2026-500397/398/399 series). Ubuntu: Fixes still in progress for 22.04 LTS, 24.04 LTS, 26.04 LTS and 26.10. Older releases (20.04, 18.04, 16.04) listed vulnerable with no published fix at last check. Package status must be verified per kernel flavour; upstream version numbers do not equal Ubuntu package versions. Red Hat Enterprise Linux 8/9/10 (including RT and related OpenShift nodes): Fix deferred. SUSE: Fixed on SUSE Linux Micro 6.2 and openSUSE Leap 16.0; other products still in progress. Always confirm against your vendor's tracker. Distribution kernels carry their own backports and versioning. Recommended actions Inventory internet-facing and multi-tenant hosts. Prioritise anything running an MPTCP listener. Apply the fixed kernel from your distribution as soon as it is available and reboot. The fix is only active after the new kernel is running. Where an immediate reboot is not possible and MPTCP is not required, disable it:
sysctl -w net.mptcp.enabled=0 echo 'net.mptcp.enabled=0' | tee /etc/sysctl.d/99-disable-mptcp.conf
Disabling MPTCP removes the demonstrated root chain surface. It does not eliminate the underlying UAF. Test the change; some applications or network setups rely on MPTCP. 4. Secondary check: sysctl net.ipv4.tcp_migrate_req (default is 0). Setting it to 0 reduces one of the vulnerable paths. 5. Monitor vendor advisories for Ubuntu and RHEL. Do not assume a kernel is safe solely because the upstream version looks recent. No public exploit code is known beyond Anthropic's lab demonstration. The combination of a 9.8 remote UAF and a published AI-built root chain against a common feature (MPTCP) makes prompt patching the correct move. Sources and scope. pwn.watch, "Linux kernel CVE-2026-98432: TCP use-after-free rated 9.8, Anthropic says its AI built a remote root exploit," 29 October 2026. The Layman Security, "Anthropic AI Built 5 Exploit Chains: Chrome, Linux, Safari," 28 October 2026. Ubuntu security tracker for CVE-2026-98432 (last updated 28 October 2026). Beacon Lab, "Alerta 2026-130 Vulnerabilidad crítica en el kernel de Linux (CVE-2026-98432)," 29 October 2026. This advisory is based on public vendor trackers, the kernel CNA record, and Anthropic's published research note. Anthropic's exploit chain is a lab demonstration; no independent confirmation of reliability outside their environment is available. Distribution patch status changes; verify against official trackers before treating any host as fixed. This piece does not treat the existence of a working public exploit as established fact.
Clayton Bax Published under ONYX Digital Intelligence Following the #OnyxAudit methodology.
X: @OnyxAudit Email: onyxdigitalintelligence85@protonmail.com https://github.com/Baximus855 @Onyx_Digital@mastodon.social
"Adjacent to true is not true." Truth has no flag nor favour, only a standard. And it's heavy!
Editors note: I use various AI agents to fetch my research. I check, strip and write the article. Facts are partly theirs. Interpretation is mine.