Cartrack Came Back Online at 07:00. That Was the Easy Half.
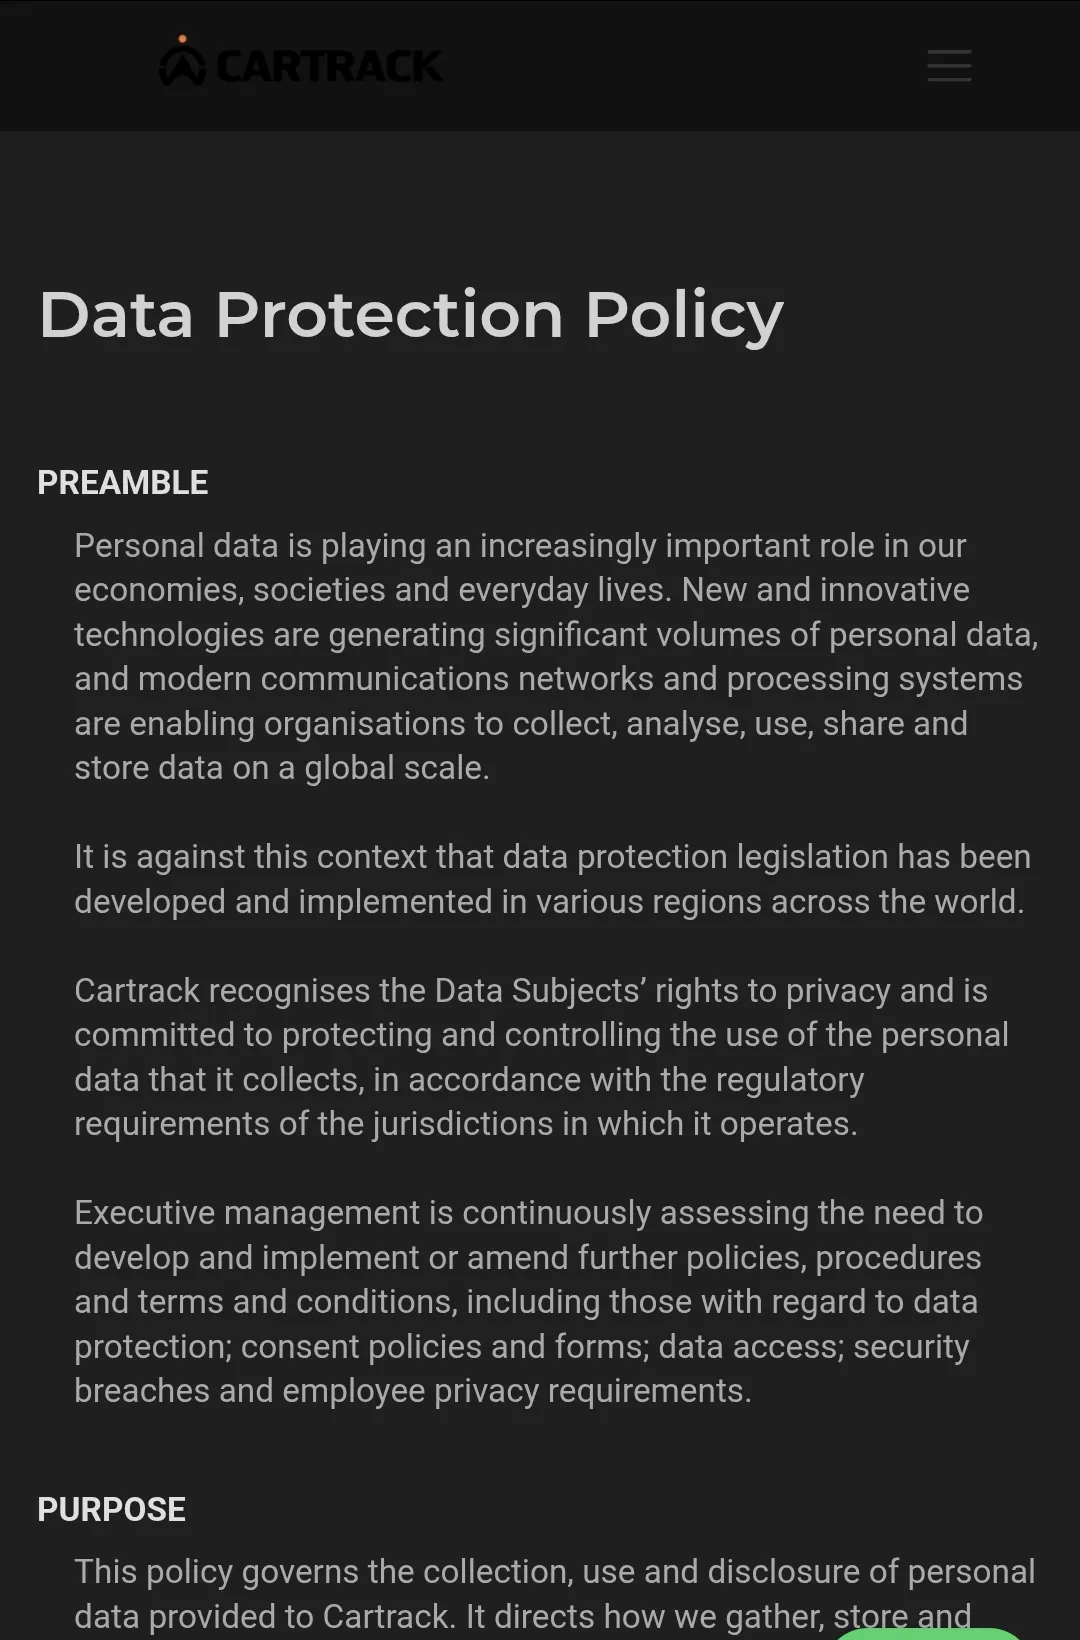
A 2.2 million subscriber tracker. A Direwolf listing. Bank and vehicle fields in the customer book. A Regulator still calling the POPIA file preliminary.
I heard about this attack through my channels at the time, and because of my long history in the security industry, I decided to hold this piece a little longer, just until the dust had settled.
It should be known that the positions in which I have worked were in essence adversarial toward the company, however you will not find any hint of that here.
I believe it has sufficiently settled now, and what I am about to put out before you is an AAR or sorts that outlines more fact than fan-fiction.
Cartrack sells a simple promise: the car can be found.
On 26 August 2026 Cartrack says ransomware hit some of its own systems around 02:00. Not a unit in a truck. The company network and the software that customers and insurers log into.
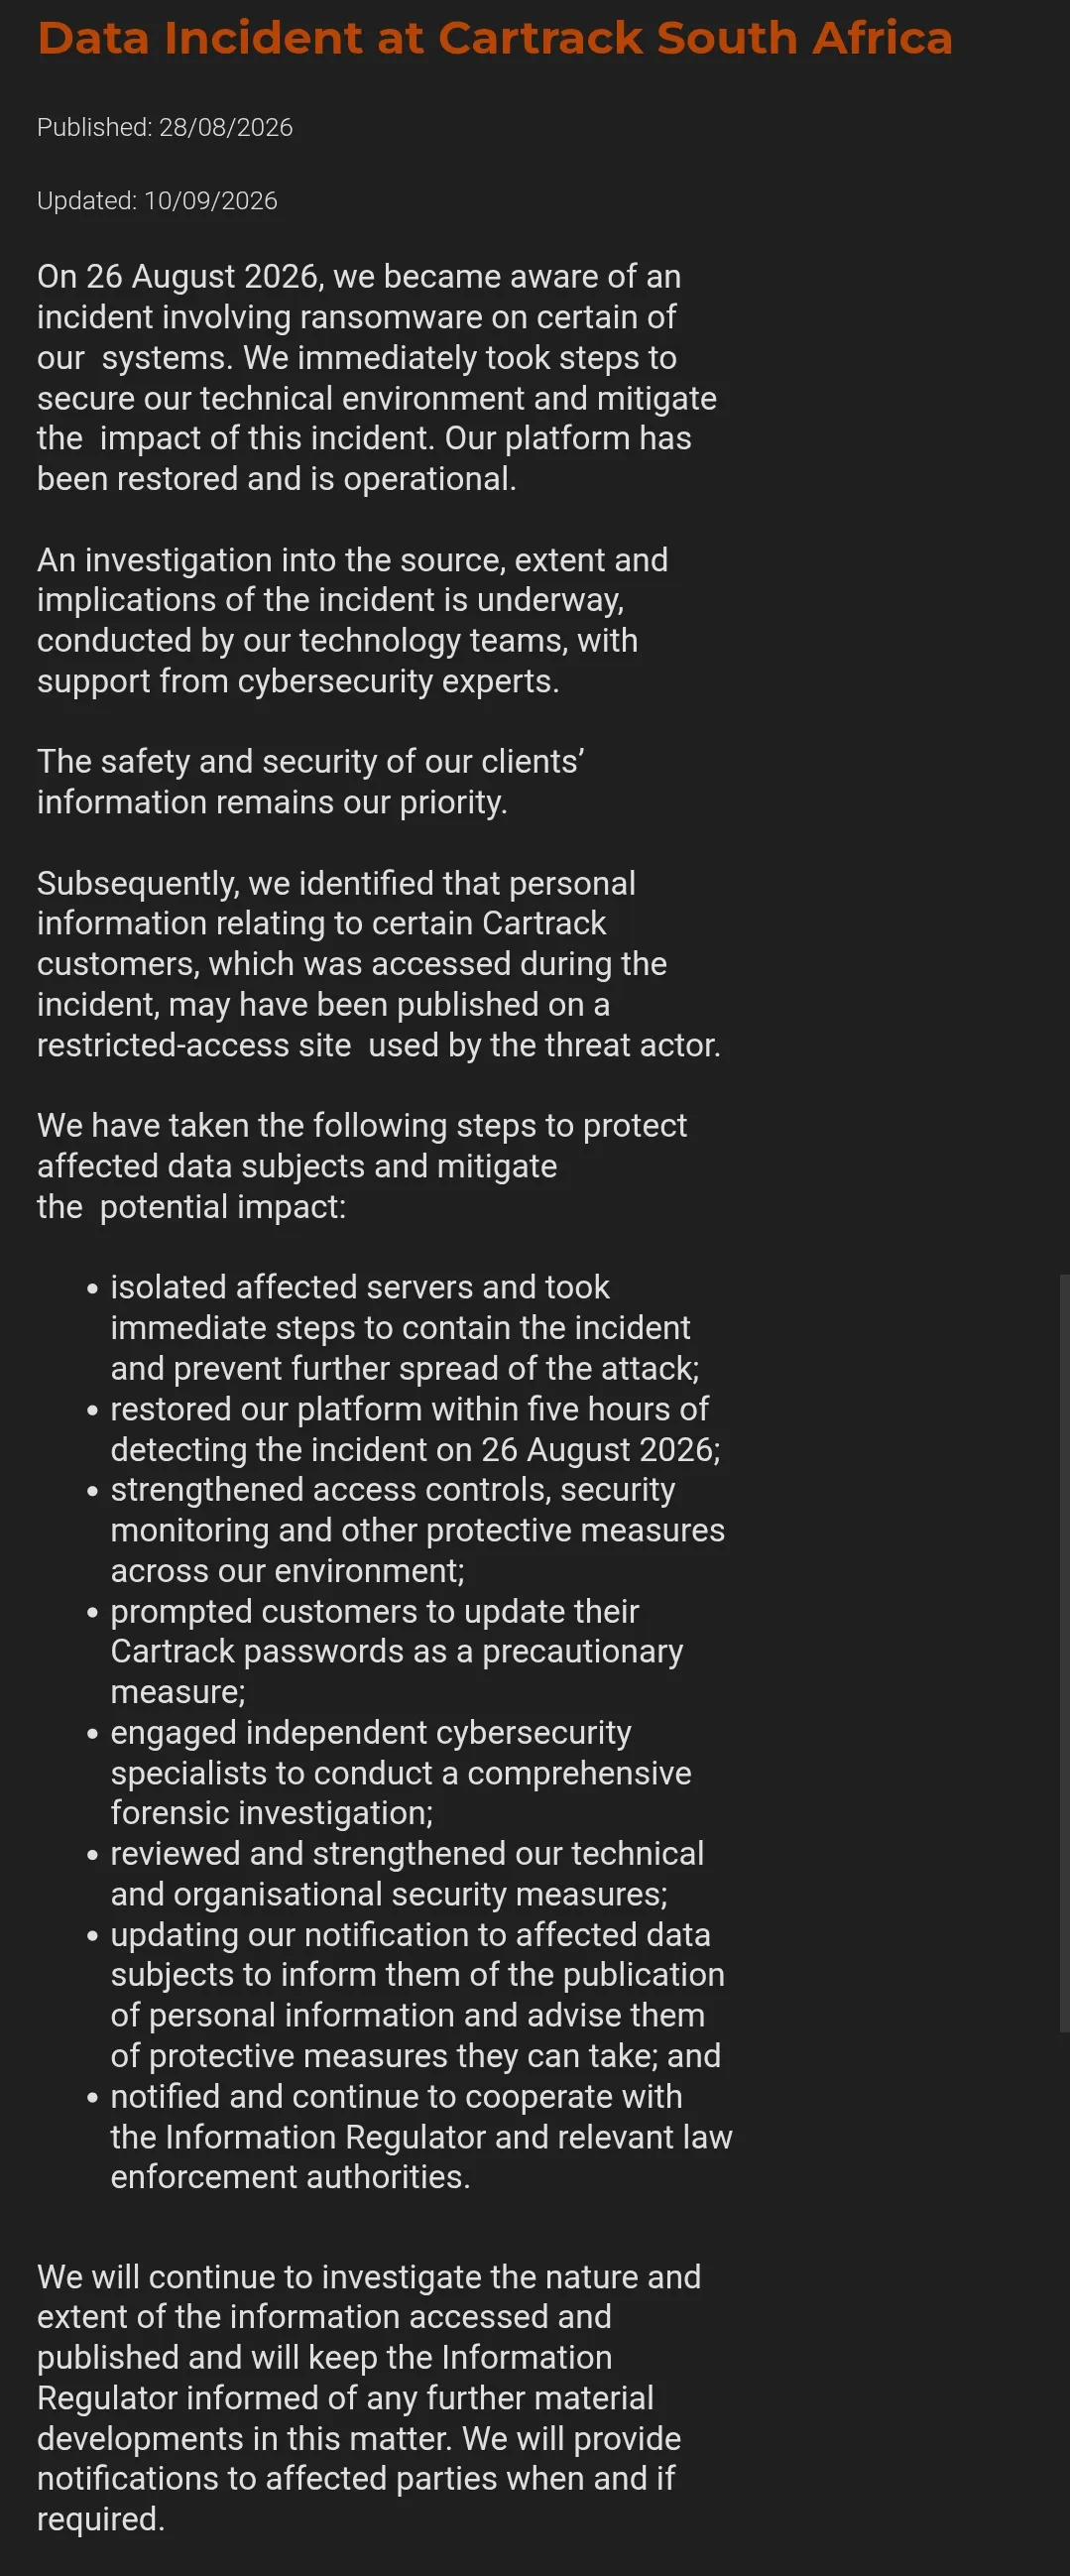
They say they cut those infected machines off from the rest of the estate so the attack would not keep moving, then brought the service back. By about 07:00 they say that platform was running again thats five hours, five hours is the uptime story.
The customer file is a different object: names, phones, addresses, debit-order bank details, and vehicle and driving fields. That file lives on the company side so turning the login page back on does not unsay a copy. Cartrack later told customers that some of what was accessed was published. Dire Wolf / Direwolf had already listed the company and that file lives on the company side thus turning the login page back on does not unsay a copy. Cartrack later told customers that some of what was accessed was published. Dire Wolf / Direwolf had already listed the company.
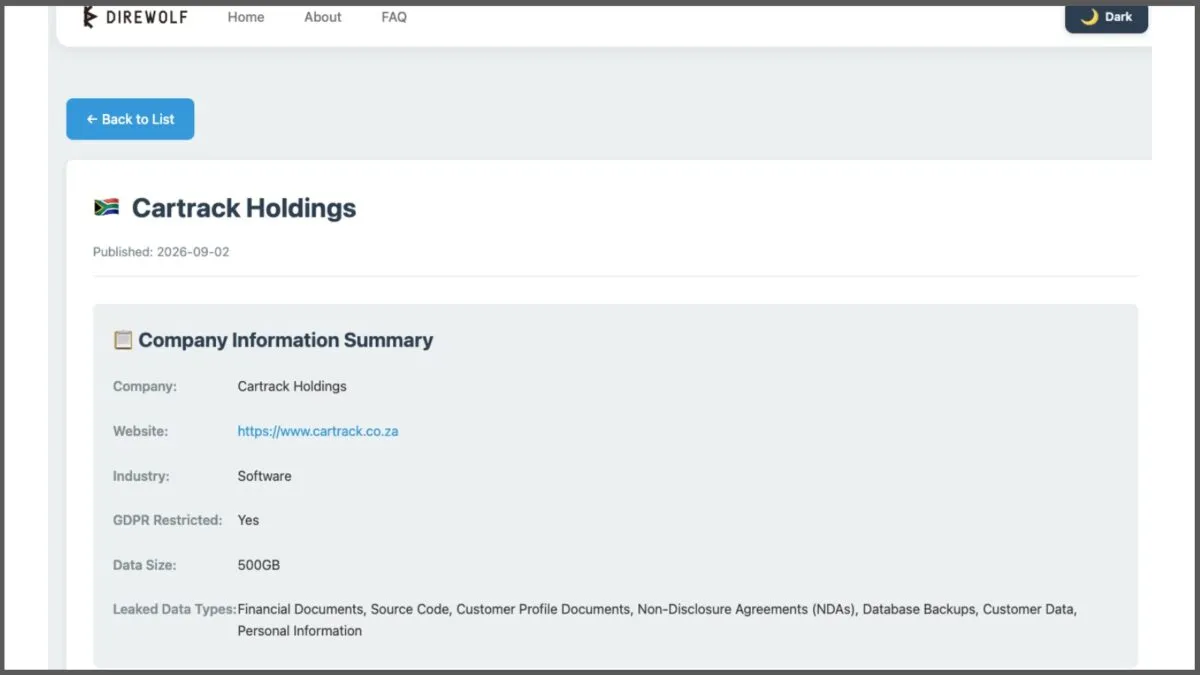 Dire Wolf listing card for Cartrack Holdings, circulated 2 September 2026. Source: FalconFeeds screenshot of the public victim card. Claimed volume is the actor’s number.
"Platform operational" means the software came back. It does not mean the customer book stayed inside the building, that must absolutely be considered burned and all customers whether or not the absolute is yet true, should take preventive and whatever curative measures available to them, before, rather than later.
The customer book is the other product. Names, phone numbers, addresses,debit-order bank details, vehicle and driving fields, PIIs SPIIs presumably, and lifestyle patterns. That book does not come back when you reboot a server and copy either exists outside the building or it does not. Cartrack later said some of what was accessed was published. Dire Wolf / Direwolf had already put the company on a leak site.
If you only read "systems restored," you read a press reflex, you need to read the file.
Who this vendor actually is
Cartrack is not a two-person GPS shop. It is the South African-facing tracking and telematics business under Karooooo, listed in New York and Johannesburg, parent results put the subscriber book at about 2.2 million on 31 May 2026. Consumer cars, entire fleets, insurance telematics to boot and a bonus U.S book as well after the 2016 expansion.
That mix is terrifying at a glance. A leak here is not only Johannesburg bakkie owners, press who looked at actor samples also described US-looking records and Karooooo's problem is multi-jurisdiction even if the first headlines were Rosebank.
The Information Regulator's problem is POPIA. (Now they are in for it) Cartrack is the responsible party for the people it signed, and Section 22 is not optional because the map came back.
What is public, in order
26 August. Ransomware on certain systems, it's subsequent containment with platform restored the same morning, the company says the Regulator and other authorities were notified that day.
28 August. First public notice. Incident confirmed, this led the Investigation "into the source, extent and implications." However, the extent of personal information accessed? "...not yet determined." This is the uptime paragraph. It is true as far as it goes. It is also the paragraph that travels furthest.
2 September. Direwolf lists Cartrack. Actor claim in reporting: on the order of 500 GB. One secondary tally has used a smaller figure. Use 500 GB as a claim, not a measured inventory. Descriptions of samples in local tech press: financial documents, source code, customer profile material, NDAs, backups, personal information. Folders shown as proof not to be confused with a full index.
8 September. Cartrack's later customer-facing line: investigation established that some information accessed in the incident was published on the actor's restricted site.
Mid-September customer mail. Attackers accessed the customer database. Information that may include names, emails, telephone numbers, physical addresses, bank-account information, and vehicle and driving-related data. Password reset asked for. Warning about phishing and impersonation. That "may include" is the legal hedge. It is also the sentence a household has to plan against, because Cartrack has not published a clean yes/no matrix per field.
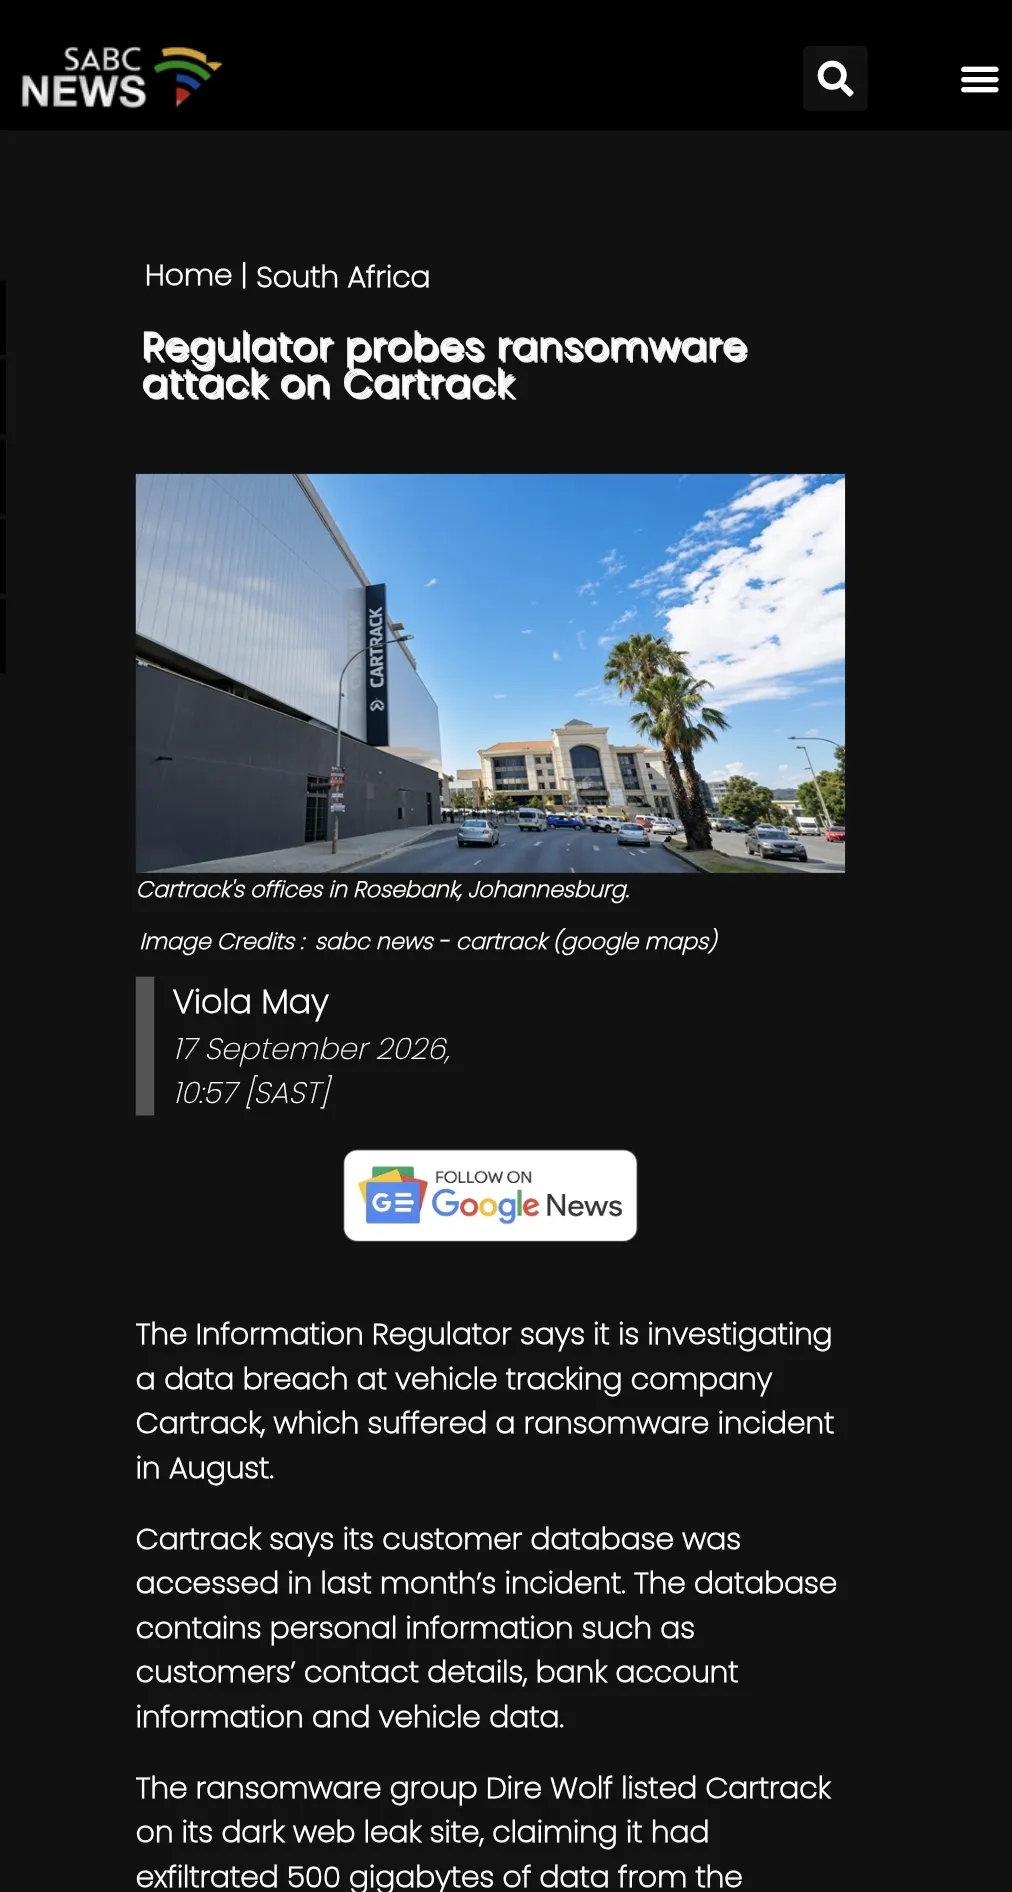
17 September. SABC speaks to the Regulator. Hangi Mbedzi: Cartrack notified under section 22. The notification is preliminary and they are still studying the extent, how many data subjects and how it happened obviously, they are in contact with the company. However one, with a little knowledge of these things can spot the forest from the trees, but without deeper insider intel anything we would devise as conclusion would be no more than guess work.
Official page. "Data Incident at Cartrack South Africa," published 28 August, updated 10 September. Isolated servers. Platform restored within five hours. Access controls tightened. Independent specialists. Passwords. Regulator and law enforcement. Still no public headcount.
That is the whole primary record. Everything else is inference.
Why a tracker book is not another email dump
Email plus phone is already enough for a convincing SMS. Add a physical address and a bank account used for the debit and you have impersonation that survives a "they guessed my name" test. Add vehicle and driving-related data and the pretext writes itself.
"Your unit is offline, pay this link to reactivate." "Insurance telematics audit, confirm the account." "We are Cartrack fraud, read me the OTP." A SIM-swap story that already knows the plate and the suburb.
I am not saying the published set contained live GPS tracks, trip histories, or "the car is in this driveway at 18:00." However I'm not saying it didn't either, but Cartrack has not said that. The confirmed class is already enough to run a local fraud week. Over-claiming turns a forensic post into a panic post, but one can speculate.
US records in the sample set, if they hold up, mean the same playbook in a second market. Fraud does not need a passport. It needs a plausible file.
Direwolf, without the folklore
Cartrack's working attribution is the group reported as Direwolf / Dire Wolf. The public fact is the listing plus the company's later acceptance that publication happened. Double extortion is the pattern: disrupt or encrypt, and copy. Paying or not paying is not the story we have but we do know about the copy.
POPIA, said like an adult
Responsible party: Cartrack.
This is their environment and their customer database, on their own notice. They do not get the MIP excuse.
Section 22 wants the Regulator told when there are reasonable grounds that personal information was accessed but customers get told when they need to protect themselves. A preliminary file means the state still does not have, in public, the two numbers that change the advice:
- How many data subjects.
- Which fields were accessed versus which fields were published.
"May include bank details" is a yellow light, imagine, and "Bank details were in the published archive" is a red light. Those are not the same sentence, until now, Cartrack has not drawn that line in public. Until they do, plan as if the yellow light is the working assumption. That is conservative.
Five hours to restore is an operations win they will keep quoting. It is definitely the wrong KPI, as far as I see it, thats exactly 5 hours too long.
Same month, same country
This sits next to MIP Holdings and the Hollard funeral-book fallout, EasyEquities / Satrix third-party notes, Cell C, Alexforbes. The two braincells left after the article and investigation I did on INTERPOL's stats on Africa are arguing one shouts the rhyme is not "South Africa is uniquely cursed." The rhyme is customer books living in places incident response can reboot, and copies living in places it cannot, the other shouts "scoreboard" and points to the fact SA has currently 92% of Africa's randsomqare attacks in the 2026 report / detections, with no signs of slowing.
Cartrack is cleaner than MIP in one respect: they are not hiding behind "it was the software middleman." They are the brand and the book. That should have made the field list faster, but it did not.
What Cartrack still has not said
These are fair questions. They are not a raid.
- How many unique customer records were in the accessed database?
- Which fields are confirmed accessed? Which are confirmed published?
- Were bank-account numbers in the published set?
- What does "vehicle and driving-related data" mean in the schema: plate, VIN, device ID, policy link, or more?
- Were fleet-admin accounts in the same table as consumer accounts?
- When was the first customer email actually sent, measured from 26 August?
- Has the US / non-SA book been notified on the same facts?
If the answers are "investigation ongoing" in week four, that is itself an answer.
If you have a unit in the car
Treat the next message that already knows your plate as hostile.
Hang up. Use the number on the contract, the box, or the official app store listing. Not the WhatsApp.
Change the Cartrack password. 2FA if they offer it. If they do not offer it, put that in the email.
SIM-swap lock at Vodacom, MTN, Cell C, or Telkom.
Watch the account that pays the debit for 90 days. New tracker fee. Insurance admin. Store card. Funeral policy you did not open.
Credit reports, free once a year:
- TransUnion 0861 482 482
- Experian 0861 105 665
- Compuscan 021 888 6000
- XDS 011 645 9100
Keep the reference number.
SAFPS Protective Registration.
One email to Cartrack, saved as PDF:
Was my identity in the accessed customer database? Which fields? Published or only accessed? What are you doing besides a password prompt?
If they go quiet: Information Regulator 0800 017 160 or POPIAComplaints@inforegulator.org.za.
Do not pay a stranger to "remove you from the dark web." The file is already copied. That product is the second scam.
Do not post your unit ID, contract number, or plate in a group chat "to see if I am in it."
Fleet managers: one mail to Cartrack on the admin book, one mail to drivers that you will never ask for an OTP, and a watch on the company debit accounts. Do not dump a spreadsheet of plates into WhatsApp.
What this post is not
It is not a claim that SAPS Cyber Crime or the Hawks buried the case. Public desks do not publish live forensics.
It is not legal advice. It is the public record plus the actions that still work if the field list is as wide as the customer mail allows.
It is not a reason to cancel a working tracker in a panic and then leave the car uninsured. Fix the account. Watch the money. Ask for the matrix.
The line
Cartrack's product is knowledge about where metal moves and who pays for the box. On 26 August they got the metal side standing again before breakfast. The who-pays side left the building and, by their own later mail, part of it was put where criminals publish proof.
Uptime was the easy half. The book is the product. Write the field list.
Sources and scope. Cartrack South Africa, "Data Incident at Cartrack South Africa," published 28 August 2026, updated 10 September 2026. MyBroadband, "Top vehicle tracking company in South Africa with 2.2 million subscribers hit by cyberattack," 7 September 2026. MyBroadband, "Cartrack warning after hackers access sensitive data," 14 September 2026. SABC News, "Regulator probes ransomware attack on Cartrack," 17 September 2026, including Hangi Mbedzi on the section 22 notification.
Karooooo / Cartrack statements are the responsible company's account. The Regulator comments are a public interview, not a final determination. The 500 GB figure is an actor claim as reported. This piece does not treat unpublished GPS tracks or a confirmed published-versus-accessed field matrix as fact.
Clayton Bax
Published under ONYX Digital Intelligence Following the #OnyxAudit methodology.
- X: @OnyxAudit
- Email: onyxdigitalintelligence85@protonmail.com
- https://github.com/Baximus85
- @Onyx_Digital@mastodon.social
Adjacent to true is not true.
Truth has no --flag nor favour--, only a standard. And it's heavy
Editors note: I use various AI agents to fetch my research. I check, strip and write the article. Facts are partly theirs. Interpretation is mine.